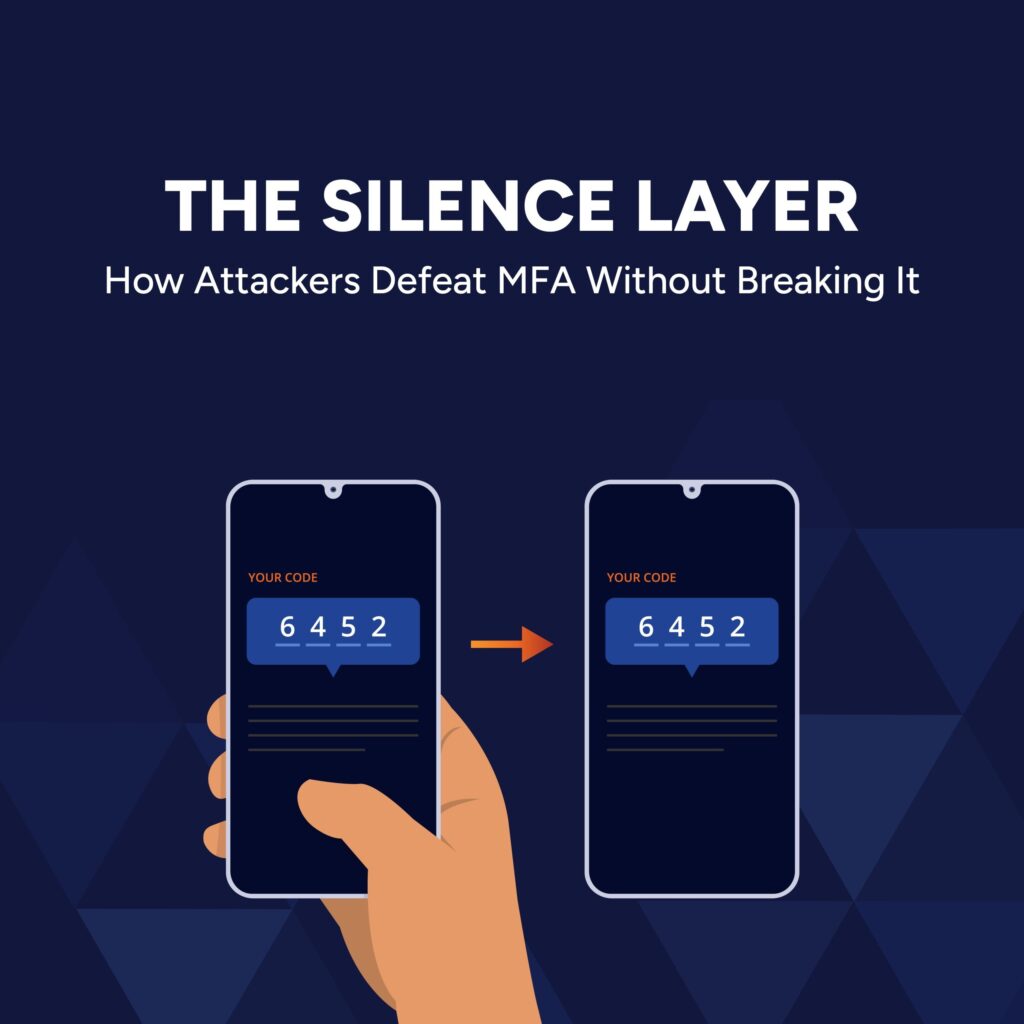
The Silence Layer
How Attackers Defeat MFA Without Breaking It
Now available on demand
A preinstalled Windows feature is quietly turning MFA into a false signal. Attackers no longer need to crack users’ MFA. They just need to make sure the user never sees it. In this webinar, Q6 Cyber’s threat intelligence team breaks down two attack patterns pulled straight from the dark web and real fraud cases:
Phone Link Hijacking: Attackers mirror a victim’s phone in real time and watch SMS codes land the second they arrive
Inbox Ghosting: Hidden email rules and manual deletions erase security alerts before the account owner ever sees them.
Both techniques produce the same result: MFA gets “approved” while the legitimate account holder is left in the dark for days or weeks – as fraud losses compound.
You’ll walk away with:
- The operational red flags that expose hijacked device pairing or a ghosted inbox
- The audit log signals your team should be monitoring right now
- The out-of-band, phishing-resistant controls that shut down these silent attacks before they cost your institution